Billy Dunn
Book 15 minutes with me. You leave with my cell.
Cybersecurity in Dallas-Fort Worth
Payroll runs Friday. No ransom note on any screen.
Most IT companies’ security plan: antivirus and hope. We close the boring doors first, and a staffed security center watches every computer.
Every computer watched 24/7/365 by a full security operations center (SOC), the kind very few IT companies offer a business your size. We close the everyday gaps first.
Think something got through? Call (817) 265-5000.
Free email spoofing check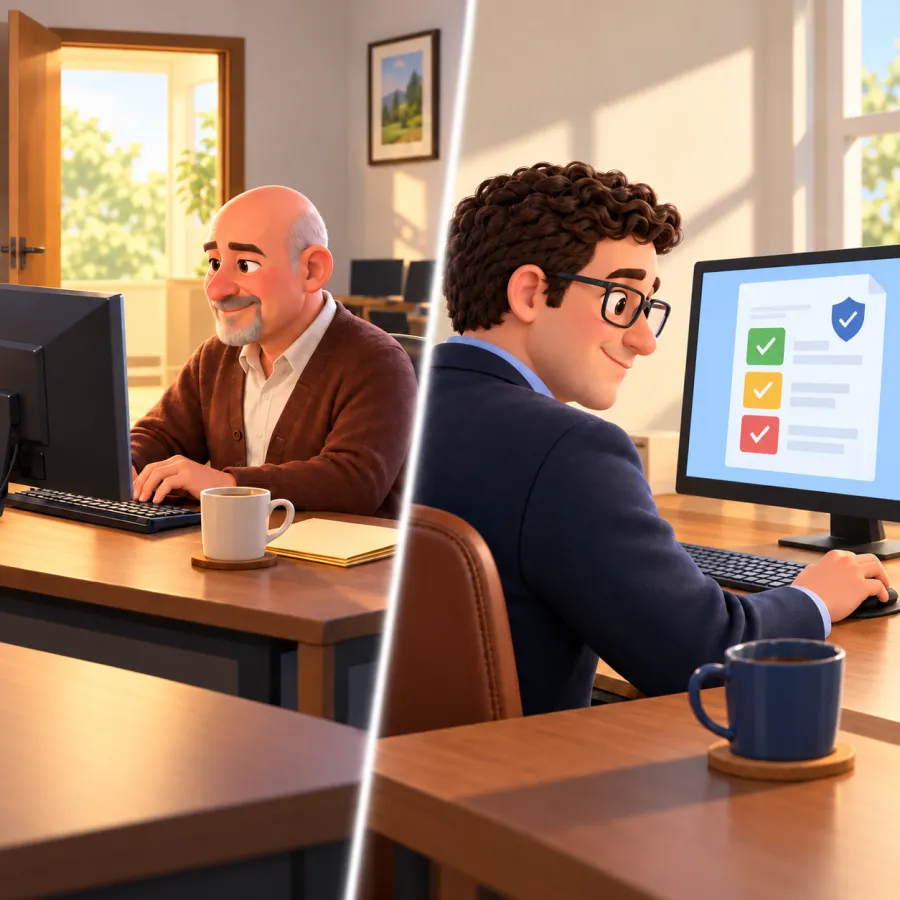 Your office
Trevor, your BDunn tech
Closing an open door before anyone noticed
Billy Dunn
Founder since 1989. Book 15 minutes with me and you leave with my cell.
Every computer, watched 24/7/365.
By a full security operations center (SOC).
The boring doors first.
Most small-business breaches are boring.
No fear-selling.
Built for a business your size.
Could someone fake an email from you?
Type your domain and see, in plain English, whether the records that make faking your email harder are set up, and how strict they are. Free, no sign-up.
A night with us watching.
6:00 PM
You go home.
We don’t stop watching. A full security operations center (SOC) takes the night shift on your systems, 24/7/365.
11:30 PM
Someone overseas tries a stolen password.
We block it, sign the account out everywhere, and have a new password ready by morning.
1:40 AM
Something nasty starts on a laptop.
We cut it off from the network within minutes, to keep it away from the rest of the office.
8:00 AM
You call. We pick up.
Call (817) 265-5000 and we pick up.
What we put in place
Multi-factor sign-in, and access by job.
A second step on everything that supports it, and each account reaches only what its job needs. One stolen password stops being the whole story.
Someone is watching every computer.
Detection and response on each machine, watched by a full security operations center (SOC), plus web filtering that stops most bad links before the page loads.
Email coming in.
Filtered, with impersonation protection.
Email going out.
SPF, DKIM and DMARC taken to enforcement, so a fake with your domain on it is easy for the other end to catch.
3 more things we look after
Patches, on a schedule.
Windows and the third-party apps, not just Windows Update.
Backups kept apart.
Isolated from the systems they protect, checked daily, and test-restored on a schedule. You can see the results.
The people.
An ongoing program, not a one-time class: short monthly videos plus test phishing emails, and you see who clicked and who finished. We walk staff through it in person when they start, and again whenever it is needed. Training is its own line on the bill. How training works.
Switching IT companies before the ransom note, not after? How we take over
It is almost never anything exotic.
A password reused from a site that was breached years ago. An invoice with new bank details. A note that looks like it came from the owner, asking for a wire. A laptop that walked out of a car.
Those are the usual ones, so that is where we start. More on how we run security.
A 2am problem gets worked at 2am, and we pick up.
When something gets through.
Contain it.
Cut it off first. Working out how it got in comes second.
Find the edges.
What was reached, what was not, told to you plainly.
Close the path.
Fix the way it came in, not just the symptom.
A password should not open every door.
What clients say
Always very responsive and very diligent in protecting our systems and being respectful of our costs.
Every review on Google: five stars.
What worries you about your security?
Free email spoofing check. Send us your domain and we’ll read its SPF and DMARC records and tell you where the gaps are that make faking your email easier. Forward us one email you sent and we’ll check DKIM too.
Or send one question. No charge, no pitch.
Already have someone doing your IT? Ask anyway.
Or email info@bdunn.com.
Got it.
Billy reads these himself. During office hours, we usually reply within an hour.
Need it faster? Call (817) 265-5000.
Rather talk it through?
Book 15 minutes with BillyPreview copy: nothing was sent.