Billy Dunn
Book 15 minutes with me. You leave with my cell.
Texas safe harbor, Chapter 542
Someone clicks the wrong link. Then the lawyers call.
Texas can take punitive damages off the table, if your security program was already in place. Most IT companies start one the week after.
Chapter 542 took effect September 1, 2025. In a lawsuit after a breach, punitive damages are the punishment on top of the actual loss. This law can block them.
Not sure it applies to you? Call (817) 265-5000.
Or ask if it applies to you first. One question is free.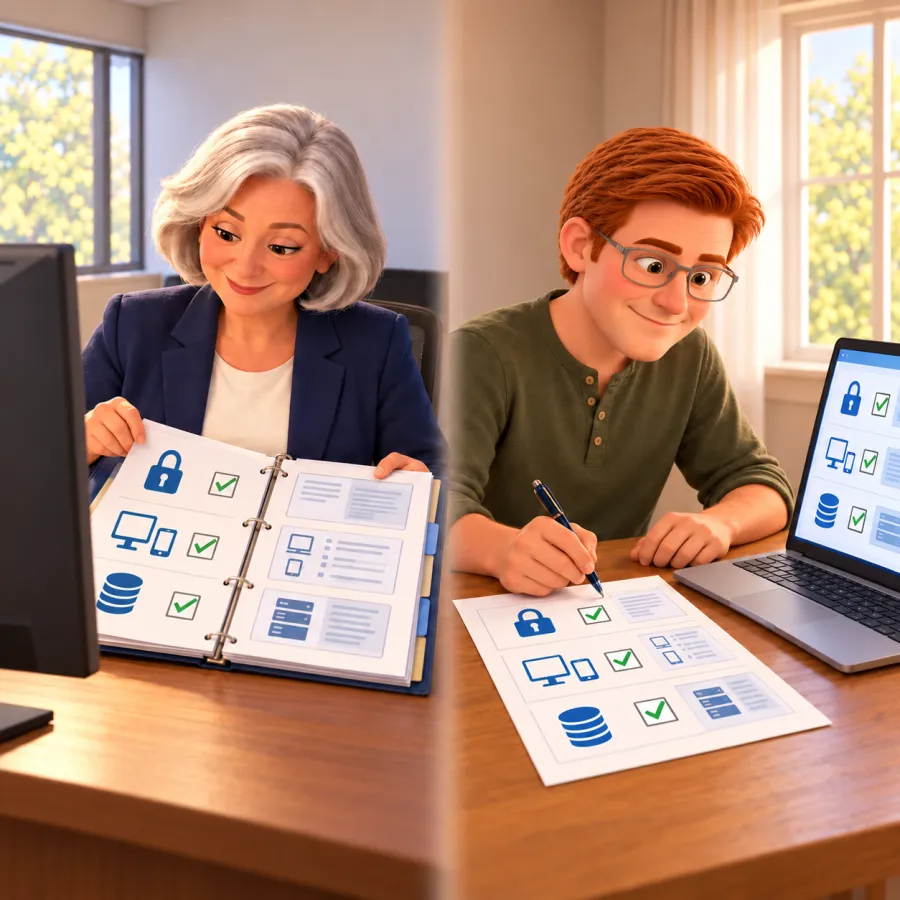 Your office
Jack, your BDunn tech
Keeping your security program running
Billy Dunn
Founder since 1989. Book 15 minutes with me and you leave with my cell.
In effect since September 1, 2025.
Texas Chapter 542.
It can block punitive damages.
Only if your program was already running.
Three yes answers.
That decides whether it applies to you.
Does it apply to you? Three yes answers.
- A Texas business.
- Fewer than 250 employees.
- You own or license computerized sensitive personal information.
Three yeses, read on. Not sure about the third one? That’s a fine first question.
What the law asks for
A Texas business under 250 employees.
That owns or licenses computerized sensitive personal information: a name with an unencrypted Social Security or license number, an account number with the code that opens it, or health records. The text: Chapter 542, definitions in Chapter 521.
Safeguards on three fronts.
Administrative, technical and physical, covering personal identifying information too. A wider net than the one that decides whether you qualify.
A recognized framework.
One the law lists, like NIST CSF, the CIS Controls, ISO 27000 or SOC 2, or something similar. No product is named, so nobody can wave the statute at you and sell you one.
Sized to your headcount.
Under 20 people password policies and staff training, at least20 to 99 CIS Implementation Group 1, at least100 to 249 the full frameworkEvery size still needs a framework.
Two words do most of the work.
Implemented and maintained. At the time of the breach, not the day you found out or the day you were sued.
You are the one who has to show it. A product bought or a policy drafted shows nothing on its own.
We do the technical work and keep the record. Your lawyer gets a written account of what is in place.
What we put in.
An inventory and a gap list.
Which systems hold what, who can reach it, what is missing, in the order we would fix it.
The controls, put in.
The work on the systems, not a report telling you to do it. Training delivered, attendance kept.
An evidence file, kept current.
What was in place and from when. We keep the receipts.
The security work comes with receipts.
What clients say
Great company if you want to protect your computer systems and keep them running and up to date. Fast response, easy to communicate with and overall great service.
Every review on Google: five stars.
Start with what you actually hold.
Or send one question. No charge, no pitch.
Already have someone doing your IT? Ask anyway.
Or email info@bdunn.com.
Got it.
Billy reads these himself. During office hours, we usually reply within an hour.
Need it faster? Call (817) 265-5000.
Rather talk it through?
Book 15 minutes with BillyPreview copy: nothing was sent.